Cell phone with image of lock on the screen.

Reasonable Security: Implementing Appropriate Safeguards in the Remote Workplace

Photo by Franck on Unsplash

In 2020, with large portions of the global workforce abruptly sent home indefinitely, IT departments nationwide scurried to equip workers of unprepared companies to work remotely.

This presented an issue. Many businesses, particularly small businesses, barely have the minimum network defenses set up to prevent hacks and attacks in the centralized office. When suddenly everyone must become their own IT manager at home, there are even greater variances between secure practices, enforcement, and accountability.

“Reasonable Security” Requirements under CCPA/CPRA and Other Laws

Under the California Consumer Privacy Act (CCPA), the implementation of “reasonable security” is a defense against a consumer’s private right of action to sue for data breach. A consumer who suffers an unauthorized exfiltration, theft, or disclosure of personal information can only seek redress if (1) the personal information was not encrypted or redacted, or (2) the business otherwise failed its duty to implement reasonable security. See Cal. Civ. Code § 1798.150.

Theoretically, this means that a business that has implemented security measures—but nevertheless suffers a breach—may be insulated from liability if the security measures could be considered reasonable measures to protect data. Therefore, while reasonable security is not technically an affirmative obligation under the CCPA, the reduced risk of consumer liability made reasonable security a de facto requirement.

However, under the recently passed California Privacy Rights Act (CPRA), the implementation of reasonable security is now an affirmative obligation. Under revised Cal. Civ. Code § 1798.100, any business that collects a consumer’s personal information shall implement reasonable security procedures and practices to protect personal information. See our CPRA unofficial redlines.
Read More
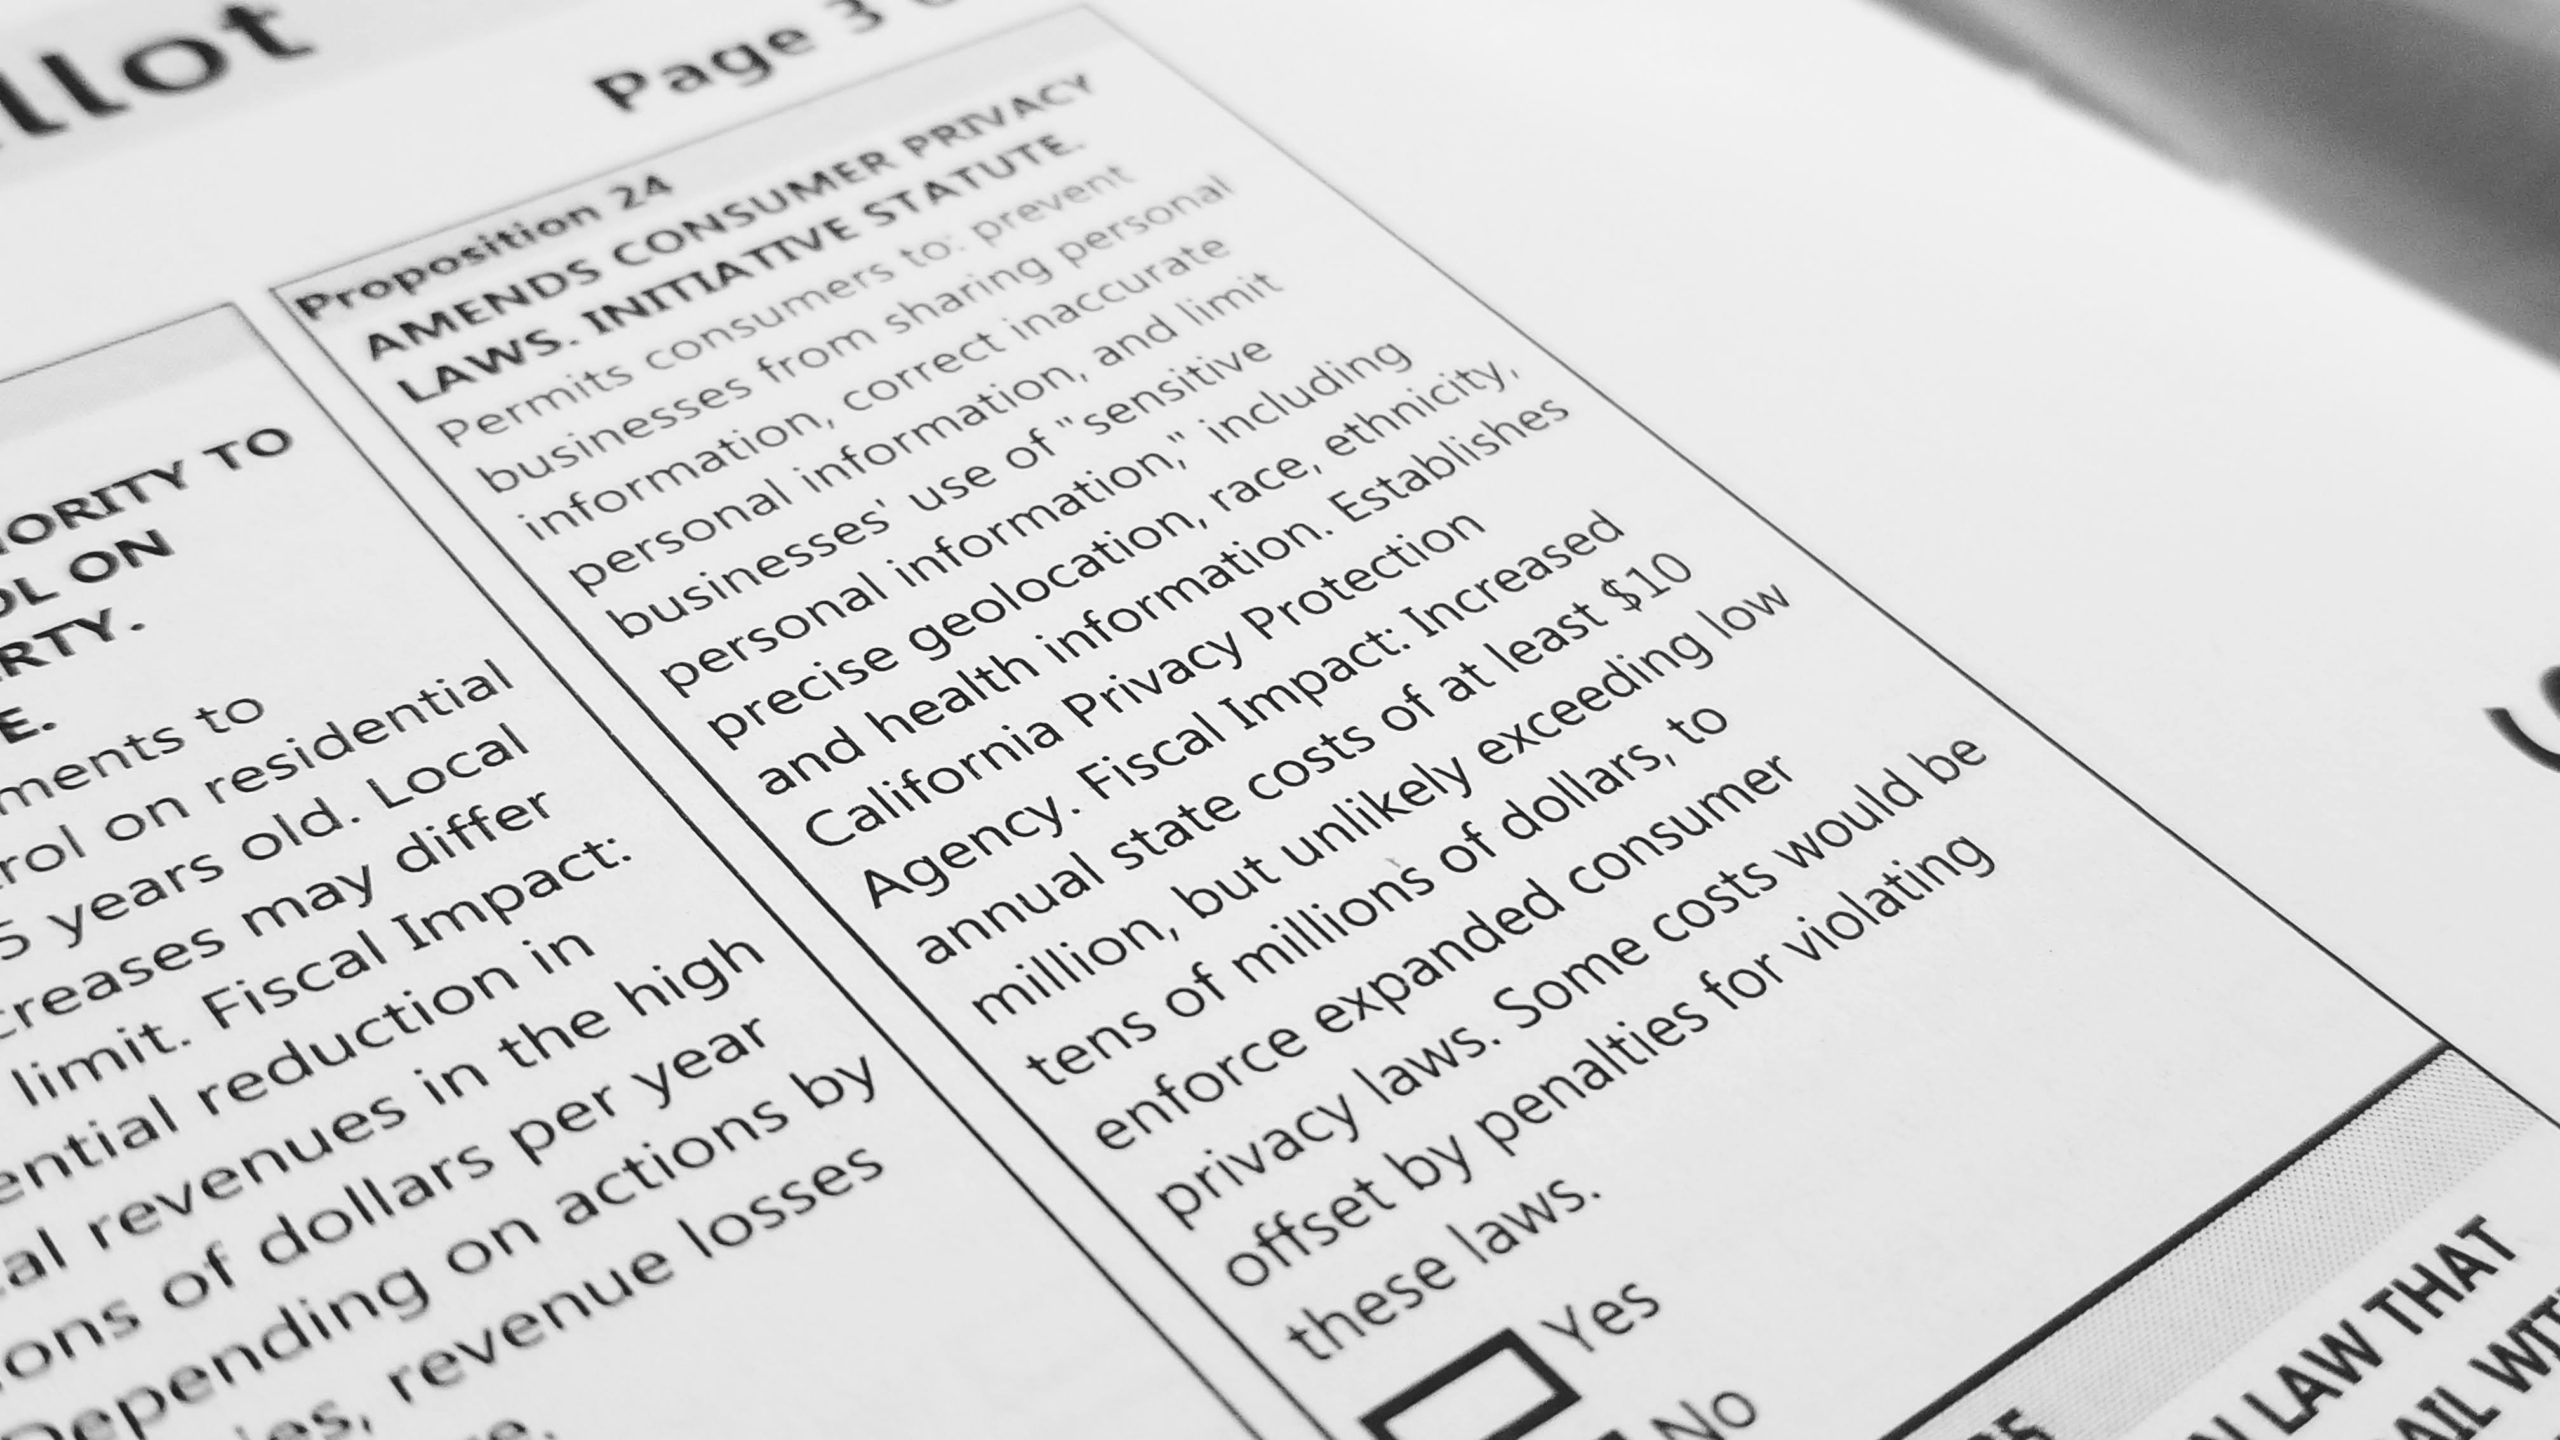
Offset angled photo of Proposition 24 from the 2020 California Voter's Guide

What Businesses Need to Know if Voters Pass Proposition 24 (California Privacy Rights Act of 2020, “CPRA”)

Hot on the heels of the California Consumer Privacy Act (CCPA), California residents this November will vote on Proposition 24. A majority yes vote on Prop 24 would pass the California Privacy Rights Act (CPRA). The CPRA proposes several amendments to the CCPA, such as granting new rights to consumers, imposing greater penalties on businesses for certain violations, and creating a new state enforcement agency, the California Privacy Protection Agency (CPPA).

1. Right to Restrict Use of Sensitive Data

Under the newly added Section 1798.121, consumers now have the right to direct businesses to limit the use of “sensitive personal information.”

As defined in CPRA, sensitive personal information appears to combine the conventional definition of “personally identifiable information” from state breach notification laws with the definition of “special category data” under the GDPR. Accordingly, sensitive personal information is data that may include a Social Security Number, driver’s license number, account log-in/debit/credit card information in combination with password or PIN. It may also include a consumer’s precise geolocation, the contents of their e-mails or texts to others, and racial, religious, biometric, or health data.

If directed to do so, businesses must limit the use of sensitive personal information to only those purposes that are necessary to provide a consumer’s requested services or goods.

To facilitate consumer exercise of this right, businesses may be required to add another link, “Limit the Use of my Sensitive Personal Information,” to their websites, in addition to any existing “Do Not Sell My Personal Information” link.

2. Right to Opt-Out of Cross-Context Behavioral Advertising

The CPRA requires a right of opt-out for “cross-context behavioral advertising” regardless of whether it constitutes a “sale” of personal information or not.

Read More
Gold gavel on platform

California Attorney General Releases Proposed CCPA Regulations

Image Credit: 3D Animation Production Company from Pixabay

California Attorney Xavier Becerra unveiled highly-awaited regulations on October 10, 2019 to enforce the California Consumer Privacy Act, a sweeping new privacy law set to take effect on January 1, 2020.

The text of the CCPA proposed regulation is available here. As a few highlights, the proposed regulation:

  • Defines “categories of sources” and “categories of third parties” to include consumer data resellers, among other types of entities. This shows the Attorney General’s increased scrutiny on data brokers.
  • Requires privacy notices to “[b]e accessible to consumers with disabilities” and “[a]t a minimum, provide information on how a consumer with a disability may access the notice in an alternative format.” This is consistent with recent trends towards ADA website compliance.
  • Requires businesses to either (1) notify consumers of the sale of their data, if they collected the data from third party sources, or (2) confirm or receive signed attestations from the source describing how they provided a notice of collection.
  • Requires greater offline rights to notice and opt-outs of sale, for businesses that substantially interact with consumers offline.
  • Contemplates a button or logo opt-out in a modified version of the regulation.
  • Recognizes the security risks of providing specific pieces of information in response to a request, with requirements around verification of identity and security of transmission.

Individuals and businesses interested in shaping the final CCPA regulations can attend public hearings or send comments by mail or email to the following:

  • Email: PrivacyRegulations@doj.ca.gov
  • Privacy Regulations Coordinator
    California Office of the Attorney General
    300 South Spring Street, First Floor
    Los Angeles, CA 90013

The public hearing dates and locations are as follows:

Public Hearing DatesLocations
Sacramento
December 2, 2019
10:00 a.m.
CalEPA Building
Coastal Room, 2nd Floor
1001 I Street
Sacramento, CA 95814
Los Angeles
December 3, 2019
10:00 a.m.
Ronald Reagan Building
Auditorium, 1st Floor
300 S. Spring Street
Los Angeles, CA 90013
San Francisco
December 4, 2019
10:00 a.m.
Milton Marks Conference Center
Lower Level
455 Golden Gate Ave.
San Francisco, CA 94102
Fresno
December 5, 2019
10:00 a.m.
Fresno Hugh Burns Building
Assembly Room #1036
2550 Mariposa Mall
Fresno, CA 93721

More information about the public hearings and proposed CCPA regulation is available on the Attorney General’s CCPA website.

Image of scale weighing human against law section code

Privacy Rights in Class Action Lawsuits

[Originally published in Orange County Lawyer Magazine, May 2019, Vol. 61 No.5.,by Lily Li and Matthew Wegner; Image Credit: kmicican from pixabay.com]

Should Putative Class Members Opt-In Before Their Personal Information Is Disclosed in California Consumer Privacy Act Litigation?

In 2020, the nation’s toughest data privacy law will take effect in California. The California Consumer Privacy Act of 2018 (CCPA) imposes harsh restrictions on companies seeking to sell consumers’ data, including statutory penalties for any breaches of data. This legislation was spurred by public outrage against the Facebook-Cambridge Analytica scandal and Equifax, Target, and Yahoo data hacks, and reflects a growing trend to protect consumer data privacy.

As with so many legislative and judicial movements in California—for example, the Save-On decision, which ushered in a wave of wage-and-hour class actions in the early 2000s, or Business & Professions Code section 17200, which before Proposition 64 was tacked-on to countless consumer class actions—the CCPA is likely to usher in a host of new class action litigation as plaintiffs (and their attorneys) seek to recover statutory damages for data privacy violations.

Read More
Pole with sign saying "future".

Privacy Law Forecast for 2019

Image Credit: ID 23689850 © Steve Ball | Dreamstime.com

This past year was quite a whirlwind for privacy and cybersecurity watchers. Just to sum up a few of the top events of last year:

  • Facebook’s Cambridge Analytica scandal rocked political headlines
  • Europe introduced the GDPR, the most comprehensive data protection legislation to date in the world
  • California enacted the California Consumer Privacy Act, becoming the first US state to create GDPR-style rules
  • Google came under fire for allowing app developers to read your email, and track your location (even with location tracking off!)
  • Marriott’s guest reservation system was hacked, exposing the personal information of up to 500 million guests, including passport numbers and payment numbers for some of those hacked

What will happen in 2019? Here are our top 5 predictions:

Read More

1 2 3